World Unicorn Riot
Icepick Leak Exposes Thousands of Homeland Security Personnel, Groups and More
Around one-fifth of Homeland Security's personnel are exposed, with thousands groups, office locations, and much, much more. The post Icepick Leak Exposes Thousands of Homeland Security Personnel, Gro
English (original) ·Read in Deutsch ⇄
Washington, DC — There’s been yet another major security breach among federal agencies. The Department of Homeland Security’s ‘single sign-on’ (SSO) login system was reportedly subverted by a hacker going by “Department of Peace” (DoP), which has revealed thousands upon thousands of federal employee records. Around one-fifth of Homeland Security’s personnel have been exposed. Offices and locations are identified in great detail, from Canadian airports to agents in U.S. embassies around the world. Groups assigned within the SSO system, going back at least to 2011, are also exposed, showing the names of globe-spanning activities, and management personnel handling undercover operations.
Thousands of personnel records include supervisors and subordinates, which enabled generating gigantic organizational charts automatically across these agencies. Combine this with the groups (some officials tagged in dozens) and one can easily browse around the highest levels of activities, including thousands of groups dealing with surveillance, special operations, finance, social media, and much, much more. Additional updates are at the end of this post.
Distributed Denial of Secrets (DDoSecrets), a U.S.-based transparency nonprofit that “archives and publishes hacked and leaked documents in the public interest,” reported the records were provided by DoP and released on Wednesday, October 28, with help from a Swiss hacktivist and journalist, maia crimew. A searchable website called icepicx.is helps dig around this data which has “been enriched” with updates according to the FAQ; the whole data set is now online. (The original domain, icepi.cx, was disabled by DHS request.)
DoP said back in March amid a leak of “details of 6,681 organizations that applied for contracts” that state violence in Minnesota — the killings of Renee Good and Alex Pretti — had motivated hacking into Homeland Security. Both of Pretti’s killers appear to be in the leaked data.
“Why hack the DHS? I can think of a couple Pretti Good reasons! I’m releasing this because the DHS is killing us and people deserve to know which companies support them and what they’re working on.”
“Email addresses and phone numbers are indispensable tools for FOIA researchers, often making the difference between a vague records request that gets stonewalled and one that gets results. Given the Trump administration’s contempt for even basic transparency, the need for such tools is urgent.”
The current tally on icepicx.is is subject to change – locations are getting combined as the data is cleaned up.
CBP is Customs and Border Protection; FLETC are Federal Law Enforcement Training Centers; FPS is the Federal Protective Service; DHS HQ is the department headquarters staff; HSI is the Homeland Security Investigations division of ICE; S&T is the DHS Science and Technology Directorate; USCIS is U.S. Citizenship and Immigration Services, and CISA is the Cybersecurity and Infrastructure Security Agency. About 9% of the people are “associates” who are consultants and contractors, often using associates.dhs.gov as a contact email domain; companies like Deloitte organizing “jump teams” figure into this world. “CTR” sometimes stands for contractor.
Many of the locations were not previously known as ICE or DHS offices. For example a suite on Parthenia Street in Northridge, California, has not been listed as an HSI office but is identified in the data. Keep in mind it could be inaccurate or out of date, but it is thought that journalists and local people will have a lot of places to check on.
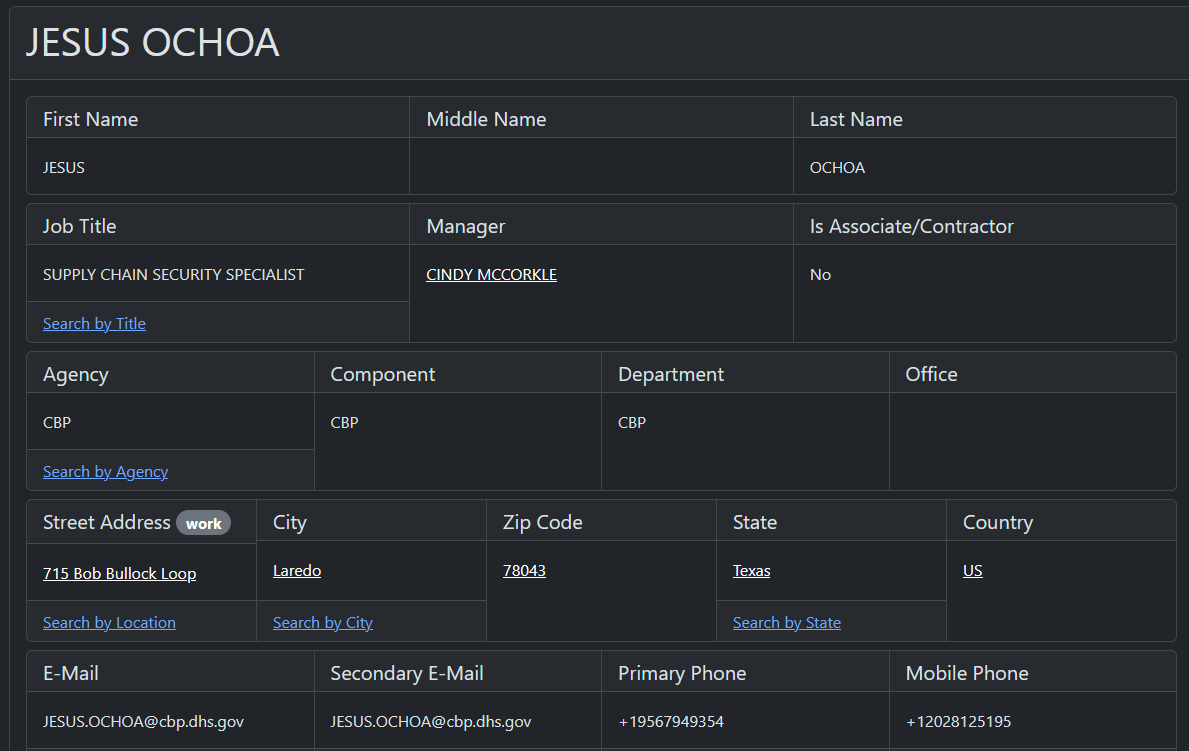
Jesus Ochoa was named as one of the agents who killed Alex Pretti, and a CBP “Supply chain security specialist” by that name based in Laredo, Texas is listed in the database, and is in various Laredo-related groups like SG-LAR029A-SEALS with more than 60 other Texas CBP personnel.
Location 0000A2, located at the Hidalgo/Pharr/Anzalduas Enrollment Center on South Stewart Road in Mission, Texas, is listed as the work site of Pretti’s other killer, Raymundo Gutierrez, who shared that space with four other “SRT OPERATOR” (an acronym for Special Response Team) and Special Operation Supervisors. A mosaic of Gutierrez’ access to DHS systems is revealed from his group memberships. For example groups called SG-AMO-EGIS-ITAK-TAK and SG-BEMS-EGIS-OFO-TAK would be used by 140 and 269 CBP personnel respectively for “Team Awareness Kit” access. (More on TAK below.)
The site notes, “This is not a comprehensive list of all DHS employees. All data is provided as-is; inaccuracies are from source data and may be reproduced.”
The icepicx.is site includes more than 20 “CUC” groups (Active Directory / Okta workgroups). (CUC is ICE jargon for “certified undercover” operations.) Each group can be checked for its individual members, which include leadership like assistant director and assistant special agents in charge, who are top personnel at individual field offices.
To name one example, the JKR HSI CUC, which would likely be a certified undercover operation group involving Homeland Security Investigations, shows personnel at “JKR – ICE COLOCATION SAN ANTONIO” which is likely an HSI office on Jackson Keller Road in the Texas city. 46 people are indexed at that location. This CUC activity also links to an office in Crystal City, Arlington, VA, called the “NGI – ARLINGTON OFFICE” with 50 people, many of whom are associated with technical programs with titles including R&D computer science, DevOps, senior data engineer, as the assigned workgroups show in exhaustive detail. (More on the Arlington office below.)
There are 26 locations linked in Minnesota (filters by state are available). For example, the Grand Marais office at 518 E. HWY 61 is listed with five Customs and Border Protection personnel.
78 personnel associated to the Whipple Federal Building are listed at Fort Snelling, MN but one person’s records are erroneously under Saint Paul. This data could be significant in ongoing federal lawsuits since plaintiffs have named anonymous government officials as “John Doe,” including a lawsuit filed over Renée Good‘s killing.
Emma Best at DDoSecrets mentioned groups that stood out like “ERO-AD REMOVAL AWARD NOMINATION SR APPROVERS” which “hits hard” because their purpose is to congratulate ICE agents for deportations. There are more than 30 groups like this.
The leaked groups are a kind of breadcrumb trail for software access controls and activities related to major websites like Twitter and Instagram.
The “Twitter.com” group includes not just “web communications,” multimedia and graphics design personnel, but many watch officers, “intelligence operations specialist” and National Operations Center (NOC) personnel. “Organizational Units” in that group include “Proxy Exceptions” which likely indicates their web traffic is handled in a special fashion — inside government agencies, data to external servers is often sent to specialized proxy computers that are controlled firewall gateways to the outside internet. The 30 members in “NOC Twitter Access” appear similar in purpose, such as NOC desk officers and senior watch officers.
Top personnel are included in dozens of these software groups simultaneously. A typical one is Citrix. Several groups include “WS1” (not to be confused with AWS, which likely means Amazon Web Services), such as “WS1-DHS-HQ-PROD-Sync-Users”. WS1 is a common federal abbreviation for Omnissa Workspace One. Major software packages are typically managed by service vendors. Just days ago Carahsoft obtained a nearly $2.7 billion blanket purchase agreement under a sole-source justification for dozens of vendors including Omnissa.
Cellebrite is a cellphone data extraction vendor which is included in the Carahsoft sole-source agreement and mentioned in two groups. The SG-EDN006A-INTEL-CELLEBRITE group has 52 members, mostly CBP intelligence officers in Texas.
The VIP List, not surprisingly, has a lot of deputy chief and director level officials, 70 in total.
The term “HQP” appears across dozens of groups, especially within the USCIS agency. Similarly “HQPRO” items are clearly procurement-based like HQPRO_ACQUISITION_SYSTEM and HQPRO_Budget. HQ1-SG-FS-HQP-RAD_Branch_Chiefs – RESTRICTED FOLDER appears with high-level personnel at USCIS.
See the section below for a quick case study on “Raven” mobile software linked to AI and privacy-sensitive personal records, research and development, and the Sandia National Laboratories.
The personnel index can be sorted by international locations as well, which are often five zeroes followed by a two-letter country code.
In London, two CBP and three HSI personnel operate from the prominent, cube-shaped U.S. Embassy at 33 Nine Elms Lane. Some agents carry the title FSNI or “Foreign Service National Investigator” as ICE or its HSI subdivision; “Mission Support Specialist” is another common title.
Three personnel, two of them investigators, are listed as in country “HN”, which is likely to mean Honduras, at the “TGK – U.S. EMBASSY” which likely means Tegucigalpa, the capital.
Brussels, Belgium, includes two officials, one of whom is a Centcom liason to “NTC-CD” and listed within CBP. That address appears to be the U.S. Embassy on Boulevard du Régent 27. (Two more HSI personnel are listed at BEG – BRUSSELS OFFICE with an unclear street address.)
Thirteen CBP personnel are listed at the Abu Dhabi International Airport in the United Arab Emirates.
Seven HSI investigators and other staff are listed at the BUE – Consular Section in Bangkok, Thailand. New Delhi, India has four HSI investigators listed. Three HSI investigators are listed in the ICE attache office in Phnom Penh, Thailand. Seven HSI personnel operate from the U.S. Embassy in Manila, the Philippines.
In Canada, 13 CBP personnel are listed at the Calgary airport. 22 CBP personnel are listed at the Vancouver International Airport and 27 CBP personnel are listed at the international airport in Toronto. Two more HSI agents are listed at the U.S. Consulate in Toronto. Three HSI personnel are listed at the U.S. Embassy in Ottawa.
Ten CBP personnel are listed at an address near the airport in Nassau, the Bahamas. Six CBP personnel are listed at the Dublin airport in Ireland. A CBP officer specializing in “Container Security” is listed at a seaport address in Tokyo. Six agents (five HSI and one ICE-ERO Attache) are listed at the U.S. Embassy in Mexico City.
The website highlights more than 50 ICE and HSI figures, including agents, officers, supervisors, managers and legal counsel based in Chicago.
We reviewed a series of records about DHS agents in Chicago courtesy of Unraveled Press, who have been probing agents that turn up repeatedly.
Martin Lagunas is in the Icepick data as a “supervisory detention deportation officer” based out of the ICE field office in Chicago. He’s listed on more than 30 groups, including “Broadview Mailbox Users”. Broadview is the notorious ICE detention facility near Chicago, and has seven other ICE agents listed, abbreviated as “BRV”. Indeed, Unraveled reporting confirmed Lagunas was highly active at Broadview.
Lagunas is also assigned BRV_Home_Drive and BRV_Share groups, which would likely be linked with Broadview data.
Along with 4100 other users, particularly deportation officers, he is on a “TACCOM LEO Users” group. 4900 users including Lagunas are on “iTAK_DHS_Interop” which is an iOS app developed by Syzygy Integration, LLC providing “Team Awareness Kit” (TAK) capabilities — think of geospatial map dots moving around with live updates to indicate where agents and perhaps targets are located.
He’s also on ERO-GOODDynamics_Import, which likely refers to the “Good Dynamics Secure Mobility Platform” provided by BlackBerry (more on BlackBerry and ICE apps below.) Along with 4550 others, Lagunas also is listed in the Headspace_users group. Headspace is a meditation app — the company landed a contract for “Funding for Mental Health Software Required for Ero Employees.”
He also is a member of WpaaS_Sunflower-Users which is likely the Sunflower asset management platform used inside ICE and DHS.
A few other entries matching Unraveled Press records: Alfredo Alvillar is listed in the records as a “1st Level Supervisor” in CBP based in Texas. He claimed to be assaulted in Chicago in an October 2025 incident. Michael Sveum, another CBP first level supervisor from El Paso, Texas, is listed; he was at the site of Renée Good’s killing in Minneapolis alongside Greg Bovino. Edgar Vazquez, another Texas CBP agent at the site of the Good killing, seems to have two entries listed in different Texas cities, with different spellings for the email address. Sveum and Vazquez were both active in fighting protesters in Chicago as well. Note that the name search requires entering “%lagunas” to search for names ending that way – the % symbol is a wildcard.
The leaks map out personnel, programs and systems at the highest levels of DHS & ICE technological research and implementation, which serves agents on American streets. A good example is deployment and development around the widely used Raven suite. “Raven” references a few products Homeland Security has developed internally, with major privacy implications for Americans. “RavenGo UEM Prod” has more than 3400 members including organizational units like “AI” within it. The “IC_raven_cloudbees_developers” group, while small, has several research & development computer science figures in it, and is colocated between the “NGI – ARLINGTON OFFICE” and Sandia National Laboratories in New Mexico. Cloudbees is an agentic coding vendor.
Raven is short for Repository for Analytics in a Virtualized Environment, which is an AI-enhanced platform. (Additionally, per an attachment on contract award HSHQDC-12-D-00014 Raven is built on Blackberry United Endpoint Management (UEM).) Raven Compliance Automation Tool is another program in the suite. The Brennan Center investigated several vendors profiting from Raven development.
There are nearly 20 “UEM” groups which include 4551 “UEM ERO Users”, who would likely be ICE deportation agents.) “UEM LEO Users” has more than 3700 members, including many deportation officers across the country. (LEO is a common acronym for Law Enforcement Organization.)
There are two entries in the database for “Christian Castro,” including an ICE agent stationed in Harlingen, Texas, where he was arrested. The #ERO HARLINGEN FLD OFC group includes 160 members and there are 119 members in the HLG – HARLINGEN FIELD OFFICE ANNEX location. However the listed email address appears to have an N as a middle initial. A CBP Border Patrol Agent in Las Cruces with the same name is also listed, without any middle initial.
Castro was charged in September by both Minnesota and the DOJ. Feds accused him of giving false statements about a January 14 shooting in North Minneapolis, which led to documents being recovered from federal vehicles amid quick nighttime protest actions.
“Black October” is the new nickname for the recent wave of critical computer security problems, preceded by the ShinyHunters hack that breached FBI personnel systems earlier this year. Is the entire idea of storing giant databases becoming too dicey?
“They’re things that Congress should have access to, but often has to ask for and fight for. Part of what makes the data so valuable is that it answers and raises questions we wouldn’t know to ask otherwise. Even if someone is unable to understand the public interest in the data, they can’t deny its value to FOIA requesters and other journalists.”
“We don’t need to look any further than recent investigations of BlueLeaks 2.0 to see that and the tendency of government agencies and contractors to conceal, minimize, and outright lie about the problems they’re creating,” Best added. Informant tipline databases including Canadian Crimestoppers run by the vendor P3 got dumped in the BlueLeaks2.0 release by DDoSecrets back in March.
In 2020, after DDoS published Blueleaks disclosures of internal police files, the group was subjected to seizures of servers in Germany. Best said,
“DDoSecrets has spent the past year quietly preparing for the regime’s inevitable crackdowns. We’ve begun the process of establishing our legal presence in European countries which still value human rights and free speech, and ensured our data is securely hosted and that the warrantless seizure following the publication of BlueLeaks will not be repeated. If the U.S. government wants to make us into martyrs, we will neither flinch nor flee from the fight. They can’t stop the signal.”
DDoSecrets provided a spreadsheet with some additional groups researchers could hone in on, grouped by likely subject areas. It is a rough snapshot, but they can all be checked out via the searchable group index. Some highlights:
AI-related groups: DHS-ChatGPT-Users, Grok.com, NRMC AI Integrated Project Team (IPT), OpenAI ChatGPT, Otter.AI, SG-ZScaler-Gemini-Access
Covert groups: #DAS Undercover Operations, CYB_Covert Operations, HQOPS_COVERT_OPS
Cyber groups: ICE-LSC Foxfire Users-SG, aws-dhs-uscis-acob-pentest-nonprod-Full-Access, BlackHat Coord, BOD 24-0X – Vulnerability Management, BOD 25-0X Known Exploited Configurations, Salt Typhoon Issue Team. Many other groups from the Cybersecurity and Infrastructure Security Agency (CISA) are also included in the leak.
Detention, asylum, removal groups: Many contain terms like DET, ERO, Removal, Detain, Detention. Including: #ERO HQ Removal, ICE-ERO-SLC-Removals-Escorts-SG, ICE-ERO-UT-Detainee-Requests-SG, DAL Detention and Removal, ICE-DET-DRO-Removals, ICE-DET-FlightOps, ICE-DET-SocialMedia, ICE-DET-Transport, Oklahoma Detained, AsylumCPMSCorrections-Full-Access. As locations, detention centers like the Moshannon Valley Correctional Facility in Philipsburg, PA are included with 8 personnel from ICE, mostly deportation officers.
Elections: 2024 General Election, CISA 2024 Elections WRG, Election Infrastructure Data Call, Elections Cyber Hygiene Validation, Indiana Elections Lines of Effort, 2026 support to election infrastructure
Events and dates: #Protect2024 Elections Services Tracker, 2018alienmigrationsurge Users, 2022 Cybersecurity Summit Planning Team, 2022 Feds Feed Families (FFF) Campaign, 2024 Super Tuesday, 2025 FIFA Club World Cup, 2025USCISPresidentialTransitionCouncil-Full-Access, 2026 FIFA World Cup Planning (R6), 2028 Los Angeles Olympics, Milan Olympics 2026, SuperBowlLX.HSI
External orgs and services: #NRC Iron Mountain-Full-Access, 4-Coginiti_Prod, Amazon Connect Internal Collaboration, Chat Google Users, BoozAllenECDTOTrainingTracking, CSA_INTEL_Palantir, CSE_CrowdStrike_Admins, Deloitte Jump Team, e-verify-feedback-Full-Access, facebook.com, HLG PALANTIR, Instagram.com, INTELVIEW CBP FOREIGN REP, KAN FEDEX_WIC – ICE, Mastodon.Social.com, MATRIX USERS, Sandia National Labs, Shodan_Website_Access, Tiktok.com, aws-dhs-uscis-r2d2-prod-Full-Access, r2d2-Full-Access
International: Bangkok-HSI-USDH-Users, Beijing Congressional-Full-Access, Counter-PRC Cyber Working Group, Cuba-USCIS-Full-Access, DAS China Initiative Access Group, HSI Panama BTMAP, HSSEDI China Ops Team, IRAD EurAsia Desk Inbox-Full-Access, IRAD-MiddleEastDesk-Full-Access
Military / suspected military: Military Info-Full-Access, SFR Military Naturalization-Full-Access, VERStratCommMailbox-Full-Access, StratComm_Calendar-Full-Access
Teams and operations: #HSI Special Operations, #HSI Special Ops, Blank Check, HQOIA_PARADOX, ICE-HSI-MIA-MFS – Cyber_Geilenfeld-SG, ICE Op White Tide USERS, ICE-HSI-MIA-MFS – Op_Capstone_MIU_OPR_Audit_03_2024-SG, ICE-HSI-MIA-MFS – Operation Los Dorados-SG, ICE-HSI-MIA-MFS-OP Hidden Fates-SG, ICE-HSI-MIA-MFS-Operation Money Flight-SG, ICE-HSI-MIA-MFS – Op_Sun_and_Moon-SG, ICE-HSI-MIA-MFS – Operation Money Garden-SG, JKR HSI Operation Condor, Ops Special Access, IEP-HSI-OP-Tri-State-Centipede, ICE-ERO-NSA-GTMO-SG, HSI SAN JUAN INTEL TEAM, IEP-HSI-Gang_Unit, Team Awesome, Team Backpay, TeamDeloitteNRMCDeliverables
Privacy, media and oversight: HQ1-SG-FS-HQU-OOP-EDITORS-PRIVACY COMPLAINTS, USCIS Privacy Complaints-Full-Access, USCIS Privacy Contracts-Full-Access, USCIS Privacy Incidents Breaches-Full-Access, HQ1-SG-FS-HQU-OOP-EDITORS-Media Disclosures
Other / misc: Aerobiology, Anti-Harassment Hotline-Full-Access, ArchangelMetabase_SSO-CRUD, HQ1-SG-FS-HQU-OOP-EDITORS-MOUs, CISA Dungeons and Dragons Club, Continuity of the Economy, CPU HYDRA, Hidden Patriot Task Force-Full-Access, HQ1-SG-FS-HQU-OOP-REVIEWERS-Dumpster Service, Megatron, MO v. Biden Discovery, OGC Crisis Cell, SerenityNow, Skynet-Admin, The Fantastic Four: OCFO Budget Formulation, USCIS Pride-Full-Access, Wraithwatch access, Writers Team :), Communications Intercept Center TechOps (CICTO) Program, HSI-Keyhole_Access, Laboremployerrelationscorresp-Full-Access, NBC Admin Restricted FOIA Data, NBC Hague SG, SDD HSI Scrum Master
10/29/2026: The Department of Homeland Security was able to get the domain icepi.cx taken offline. the new domain icepicx.is is currently working and links here updated. The Bluesky social media network blocked outgoing links to the the site domains according to TechCrunch, even though the data only includes official phone numbers and email addresses. TechCrunch attributed the domain suspension to a DHS vendor called ZeroFox. DDoSecrets announced an Icelandic backup website address as well. The Icelandic host flokinet has rebuffed the ZeroFox attempt to take the site down, refuting the claim that business contact records are “doxxing.” Coverage hit Wired, and the Washington Post confirmed authenticity of records. Reuters, NextGov, NBCNews, CNBC, The Guardian, TechCrunch, TechDirt, TechRadar, NPR, LA Taco, BBC, and Techspot released detailed reports.
On the WBAI show Off the Hook, Emma Best said that the issue was a configuration problem with Okta: “From what little I understand about the actual breach itself, the Department of Peace found and exploited a configuration error in DHS’s Okta service and I’m fairly certain that error would be on DHS’s end and not Okta’s simply because that is usually how it works. The issue seems to be limited to DHS and that seems to match what Okta has been saying.”
Please consider a tax-deductible donation to help sustain our horizontally-organized, non-profit media organization:
Follow us on X (aka Twitter), Facebook, YouTube, Vimeo, Instagram, Mastodon, Threads, BlueSky and Patreon.